Cybersecurity’s Black October: How to protect yourself
Cybersecurity professionals are having a brutal month.
What’s being dubbed Black October isn’t even over, and it’s already brought about several dozen major cyberattacks and AI-identified vulnerabilities across the internet.
When critical vulnerabilities in PHP, the programming language used by around 70% of websites, were uncovered with the help of AI tools and disclosed by the PHP Foundation on Oct. 21, the race to patch servers around the world began.
Cloud services provider Cloudflare reported millions of attempts to exploit the vulnerability after its disclosure, following thousands of attempts in the preceding hours.
Some countries, including France and Finland, temporarily pulled access to certain websites while the US National Security Agency (NSA) warned organizations to patch the flaws immediately or take affected systems offline.
“We are at Security Armageddon now,” said NEAR founder Illia Polosukhin. Anthropic’s chief security adviser Jason Clinton warned that, “as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better.”
Citizens of the United Kingdom are even being urged to “be ready” for an emergency, such as severe weather or cyberattacks, that could cut off access to critical infrastructure such as water, electricity or the internet. US military installation have been told to prep for 90 days of independent operation under the FORTRESS initiative.
Houston, do we have a problem?
Beyond rushing out to stockpile canned food and walkie-talkies, is there anything else ordinary people can do to mitigate their exposure?
So how bad is Black October, really?
“It’s really bad. It looks like the rest of the internet is waking up to the reality we had three months ago,” Rob Hamilton, a Bitcoin security researcher involved in the Bitcoin Red Team, tells Magazine.
UK government is urging citizens to be ready for an emergency. Source: gov.uk
In the past week or so, cloud platform Railway disclosed that an attacker has accessed and decrypted customer credentials and API keys, apparently targeting AI providers.
Related: France is world’s most dangerous place for Bitcoiners: 90 attacks in 7 months
Medical testing giant Quest Diagnostics confirmed a breach of private patient health data, while Indian security firm eMudhra was found to have eight digital certificate authorities with weak keys that could potentially have let attackers impersonate trusted websites. And code hosting platform GitHub experienced a major service disruption that highlighted how heavily the software world relies on shared infrastructure.
GitHub’s senior director of security, Austin Devers, says incidents like this are a “clear reminder that reliability requires constant work,” because modern development is “so connected.”
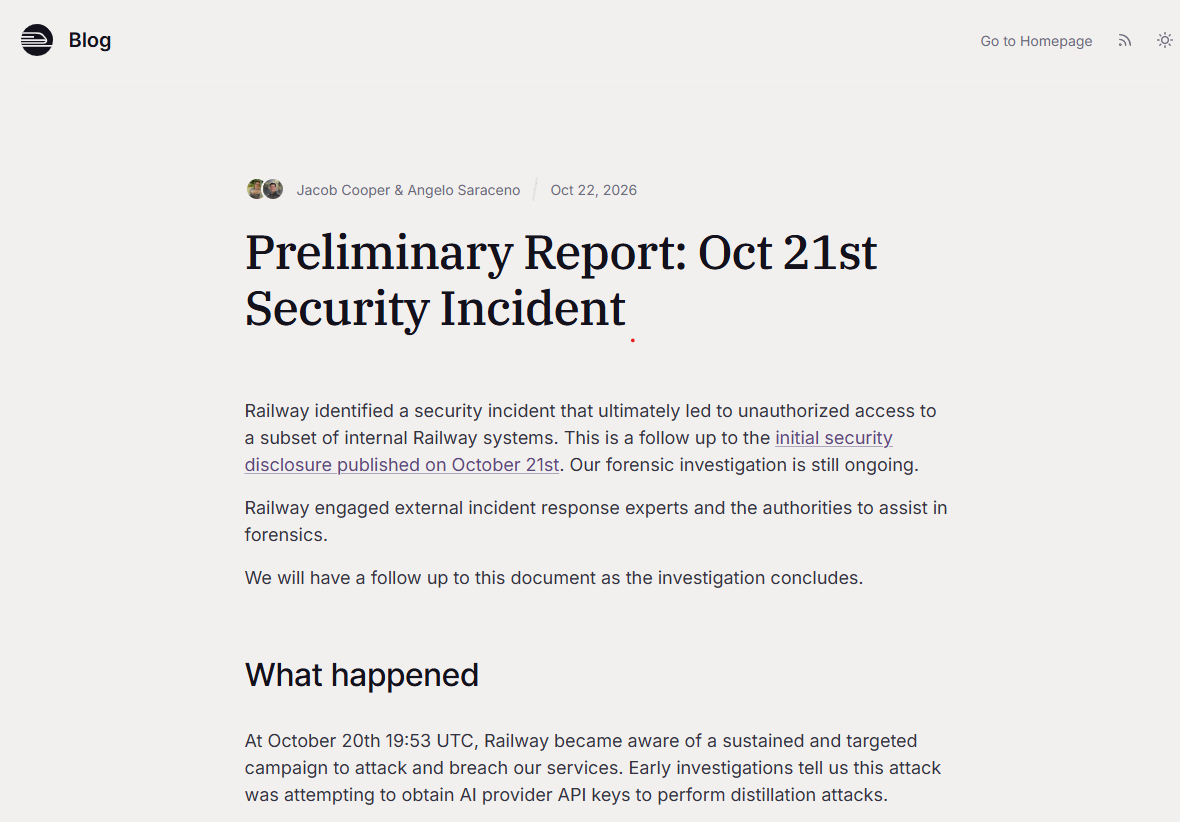
Railway security incident. Source: Railway
Jonathan Riss, an OSINT and blockchain intelligence analyst at blockchain security firm CertiK, tells Magazine:
“What concerns us most is how a single weakness in shared infrastructure can expose many organizations simultaneously.”
Unfortunately, he adds that AI’s ability to find vulnerabilities is not matched by its ability to fix them:
“Finding vulnerabilities faster does not automatically give us the capacity to resolve them faster.”
Why things are likely to get worse
One reason the problem is getting worse is because AI has changed the economics of cybersecurity.
What once required nation-state resources and sophisticated hackers to pull off can now be achieved by a teenager in a basement somewhere.
AI entrepreneur and investor Matt Shumer said that AI enables non technical users to find weak spots and exploit them, leaving defenders are “racing to keep up.”
“Every weak spot still has to be fixed, tested and installed on millions of systems run by people who are already stretched thin.”
Devers says AI-assisted security tools are “dramatically” lowering the barrier to “uncovering complex, deep-seated flaws in widely used codebases.”
Related: Keystone says website breach exposed hardware wallet buyers’ addresses
What can ordinary people actually do?
There are some practical steps ordinary folk can use to stay safer online during this volatile period.
The internet is under attack. Source: Matt Shumer
Shumer recommends staying off sites you don’t know, and definitely don’t enter passwords or card numbers into unfamiliar sites “until this blows over” since smaller sites are the “least likely to have patched.”
Delete any apps you don’t use and unplug smart gadgets you don’t need. Keep some cash at home and enough groceries for a few days, “if you want to be extra careful.”
Devers says the best defense is “locking down personal access points and keeping overall footprints small.” Turn on Multi-Factor Authentication (MFA) across all accounts, ideally using an authenticator app or hardware security key rather than text messages.
“This acts as a circuit breaker and stops hackers from logging into your account even if the underlying software is compromised.”
Never reuse passwords either, he says. “Create strong, unique passwords for every site, and periodically disconnect old app permissions or third-party connections you no longer use.” Keep your devices and web browsers updated automatically:
“While platform teams work to fix cloud-level security issues on the backend, keeping your devices secure ensures hackers can’t use your personal hardware as a back door into your accounts.”
To self-custody or not self-custody, that is the question
While the alarming rise in security incidents has caused some crypto holders to consider alternatives and some experts to advise against self-custody, others, such as Bitcoin advocate and Casa chief security officer Jameson Lopp, remind users that defeats the whole purpose.
“You can only benefit from Bitcoin’s unique properties when you hold your own keys. [...] Giving up your keys doesn’t make the risk go away, he says. It moves the risk somewhere you can’t see or control.”
Riss recommends separating small amounts you intend to use into a hot wallet, from longer-term holdings in a hardware wallet, and to “actually read what you’re signing rather than approving blind.”
While these precautions can reduce your vulnerability to attack, everyday users can only lock down local issues, and have little ability to affect wider problems.
You can “reduce blast radius,” he says, “not prevent infrastructure compromise.”
So while users can improve their cyber hygiene, ultimately, “the structural burden sits with platforms and providers.”
Magazine: Scammer loses $4.8M stored on tampered Ledgers: Asia Express